
Google Workspace can be a practical intake and review layer for corporate gifting, but it should not become the invisible system that owns eligibility, money, recipient consent, fulfillment, and audit evidence all at once. A durable design separates human decisions from automated dispatch, gives every event a stable identity, and makes failure visible before anyone resubmits a row and accidentally sends a second gift.
Decide what Google Workspace should—and should not—own
Start with the business boundary, not the script. A request may originate in the Google Forms API, appear in a review sheet through the Google Sheets API, and trigger logic in Google Apps Script. None of those components should decide whether a payment is legal, whether a recipient owes tax, or whether a country can be served. They can carry a decision that accountable people and governed systems have already made.
Use Forms for structured intake, Sheets for a transparent work queue, Apps Script for narrow orchestration, and the gifting platform for recipient experience and fulfillment. Keep the policy engine, budget authority, identity administration, legal interpretation, and payroll treatment outside the sheet unless those responsibilities are explicitly assigned and controlled. A cell color is not an approval record. A copied tab is not a backup. A successful script response is not delivery.
Write a one-page service charter before building. State eligible occasions, requesters, approvers, budget sources, supported recipient types, required evidence, and excluded uses. Define the record of decision: for example, an approval event containing approver identity, timestamp, policy version, budget code, recipient reference, and request hash. This prevents the automation from quietly acquiring authority that nobody intended to delegate.
The most important operating rule is simple: Workspace may collect and coordinate, but the system of record for each fact remains named. Employee status belongs in the authoritative people system; customer eligibility belongs in the relevant commercial system; budget availability belongs in finance; fulfillment status belongs in the execution layer. The sheet holds references and a reviewable snapshot, not a competing master record.
Assign one owner to every stage and data object
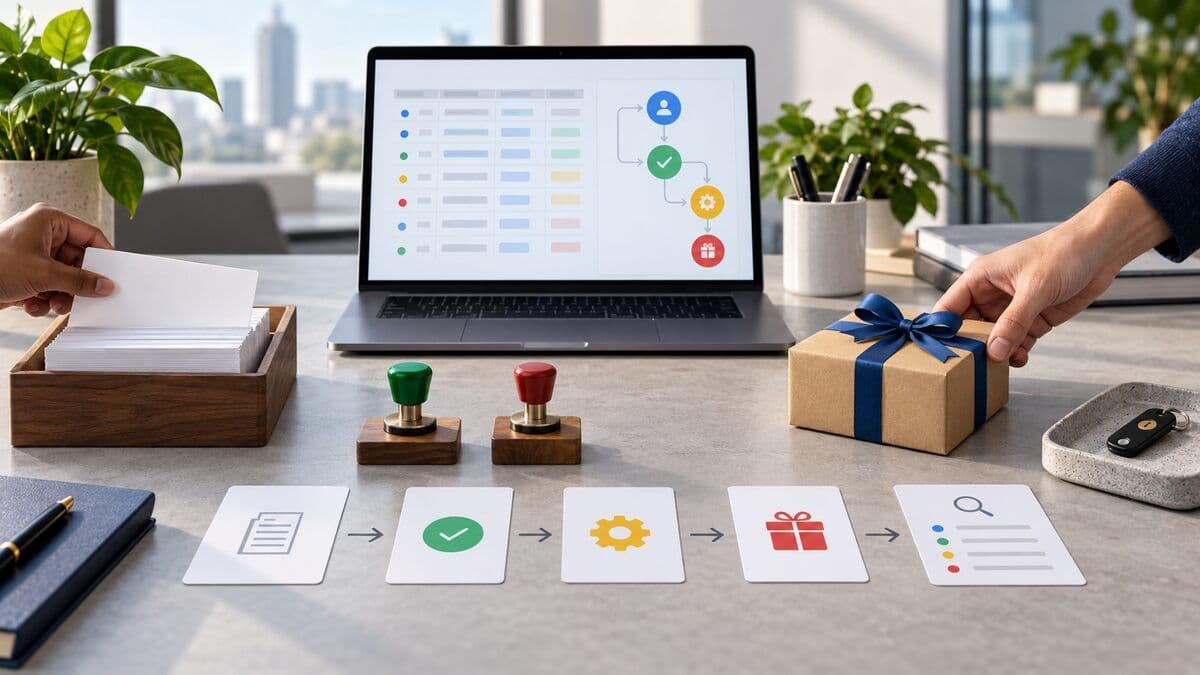
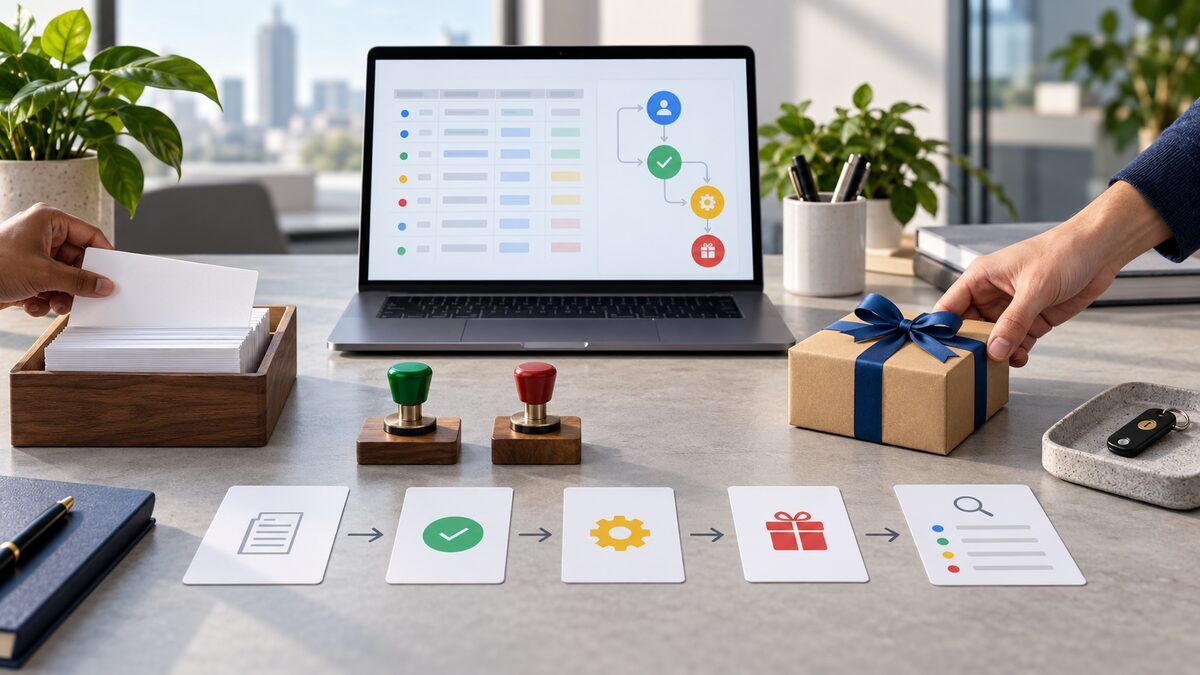
A reliable workflow has five stages: intake, enrichment, approval, dispatch, and reconciliation. Each stage should have one accountable owner and a defined handoff. When ownership is shared vaguely between HR, IT, events, procurement, and finance, exceptions remain in private messages and the spreadsheet becomes impossible to reconcile.
Table: responsibility boundaries for a controlled gifting workflow.
| Stage | Primary owner | System action | Required evidence |
|---|---|---|---|
| Intake | Program operations | Validate required fields and consent path | Request ID, requester, purpose, policy version |
| Enrichment | Identity or data owner | Resolve stable recipient reference and market | Lookup result, source, timestamp, confidence |
| Approval | Budget and policy approver | Approve, reject, or return for correction | Named approver, decision, reason, budget code |
| Dispatch | Automation service owner | Send one idempotent request to the execution layer | Event key, request hash, response ID |
| Reconciliation | Program operations and finance | Match accepted, claimed, shipped, delivered, failed, and refunded states | Status history, amount, exception owner, closure |
For each object, distinguish display fields from control fields. A recipient name is useful to reviewers; a stable employee or customer ID is safer for deduplication. A human-readable campaign name helps operations; a machine event key protects retries. A delivery country guides routing; an address should normally be collected through an appropriate recipient-controlled experience rather than exposed in a broad internal spreadsheet.
Minimize the sheet. Reviewers may need occasion, business purpose, region, budget band, requester, approver, and status. They often do not need a home address, personal phone number, gift selection, or detailed fulfillment history. Add a retention period to every column class. If a field has no decision purpose or reconciliation purpose, remove it.
Treat the spreadsheet as a queue with a schema, not a canvas. Freeze column names, document allowed values, protect control columns, and reject rows with unexpected fields. Use data validation for human inputs, but validate again in code. A user with edit access can paste invalid values, reorder columns, restore an old version, or copy formulas. The dispatcher must read by stable header names and enforce a schema version before taking action.
Design intake for consent, correction, and safe defaults
An intake form should ask only what the requester can legitimately provide. For an employee milestone, the requester might supply the employee identifier, occasion, milestone date, program code, and business justification. The recipient should provide delivery details and preferences through a later controlled invitation when possible. For a customer event, the requester may supply a CRM reference, organization, relationship owner, event, country, and approved budget.
Do not ask a requester to paste a sensitive address into a free-text field just because it is convenient. Free text is difficult to validate, easy to overshare, and hard to delete selectively. If the business truly needs an address at intake, separate fields, explain purpose and retention, restrict the response destination, and document who can view it. Consent for marketing is not the same as consent for fulfillment.
Add correction paths before automation. A requester should be able to see that a row is NEEDS_INFO, understand which field failed, and correct it without creating a second request. The workflow should preserve the original request ID and revision number. A resubmitted form that generates a fresh row can create duplicates unless the old request is explicitly canceled.
Use safe defaults: no dispatch when eligibility is unknown; no budget code means no approval; no market mapping means manual review; no policy version means rejection; an ambiguous identity lookup never chooses the first similar name. The cost of waiting is usually lower than the cost of sending a gift to the wrong person or exposing a recipient’s information.
Google Forms API notifications can be delivered through Cloud Pub/Sub, but the notification contains identifiers rather than detailed response data, so the application must fetch the current record. Watches expire after one week and must be renewed. For a smaller workflow, an installable form-submit trigger may be simpler; it runs under the account of the person who created it and is subject to Apps Script quotas. Record that operating identity and plan for employee departure, credential review, and trigger replacement.
Use identity lookup as verification, not authorization
The Admin SDK Directory API can help verify that an employee reference maps to an active account, organizational unit, or permitted attribute. It should not become a reason to grant broad domain administration to a gifting script. Use the read-only user scope when retrieval is sufficient, and return only the fields needed for the decision.
Under Google OAuth 2.0, request scopes incrementally and only when the related feature is used. Google’s guidance also recommends storing client credentials in secure storage rather than hardcoding or committing them, protecting user tokens at rest and in transit, and revoking tokens when they are no longer needed. Document who owns the OAuth client, consent screen, project, service account, delegation setting, and revocation procedure.
Avoid using email address as the only identity key. Aliases change, names collide, and contractors may use external domains. Store a stable source identifier plus the source system. If a directory lookup is optional, make failure explicit: IDENTITY_UNVERIFIED is safer than silently proceeding. If a manager submits on behalf of someone else, record both requester and recipient references.
Separate lookup permission from dispatch permission. The component that reads a directory should not automatically hold the secret or token needed to create gifts. A narrow dispatcher can accept an approved, minimal payload after policy checks. This separation limits the effect of a compromised form, sheet, or script account.
Review access quarterly and after role changes. List sheet editors, form collaborators, Apps Script project editors, trigger creators, OAuth client owners, Cloud project administrators, and gifting-platform credential holders. Remove stale access, rotate secrets according to policy, and test revocation. Least privilege is not a one-time configuration; it is an operating process.
Make approval a state machine, not a checkbox
A checkbox labeled “Approved” is easy to understand but weak as a control. It does not prove who changed it, which version was reviewed, whether the budget was still available, or whether the row changed afterward. Build an explicit state machine and append decision events rather than relying on appearance.
Table: minimum states and transitions for one gifting request.
| State | Who may enter it | Required checks | Permitted next states |
|---|---|---|---|
| DRAFT | Requester | Required fields present | NEEDS_INFO, SUBMITTED, CANCELED |
| SUBMITTED | Validated intake | Schema, identity, policy reference | NEEDS_INFO, PENDING_APPROVAL, REJECTED |
| PENDING_APPROVAL | Workflow service | Budget and approver routing | APPROVED, REJECTED, NEEDS_INFO |
| APPROVED | Named approver | Request hash unchanged | DISPATCHING, CANCELED |
| DISPATCHING | Dispatcher | Idempotency key reserved | ACCEPTED, RETRY_WAIT, FAILED |
| ACCEPTED | Execution response | Provider response ID stored | IN_PROGRESS, CANCELED |
| CLOSED | Reconciliation process | Final status and financial evidence | None |
Compute a request hash from the approved control fields. If any of those fields changes after approval, move the request back to review. Do not let an operator change the amount or recipient while preserving the old approval. Cosmetic notes may remain editable, but control data should be protected or versioned.
Use two-person review when the risk justifies it: high values, public officials, regulated recipients, sensitive occasions, unusual countries, or manual address handling. Two people should not merely tick two adjacent boxes; each decision should carry identity, timestamp, policy version, and reason.
Budget reservation should occur before dispatch. The workflow can reserve an amount against a program ledger, then release or adjust it after final reconciliation. If the sheet is only a review surface, the ledger should remain in the financial or program system. Preventing duplicates is not enough if several legitimate requests overspend the same budget.
Prevent duplicate gifts with idempotency and locks
Installable triggers can overlap. A user may click twice, a network request may time out after the provider accepted it, or two editors may move a row at nearly the same time. Apps Script also has execution and daily quotas; a single execution is limited, so large queues should be processed in bounded batches with resumable state.
Create an idempotency key from stable business facts, not the current row number. A useful pattern is program:recipient:occasion:effective-date:version. Store the key before the external call, and include it in the request to an execution layer that honors idempotency. If the call times out, query by the same key or provider response reference before retrying.
Apps Script LockService can prevent concurrent code from modifying a shared resource. Use a script lock around the small critical section that checks and reserves an event key; do not hold it during a slow network call. PropertiesService can store small key-value state, but its values are strings and its capacity is limited. It is suitable for cursors, configuration references, and compact reservations—not a complete audit database or a vault for secrets.
function reserveEvent(eventKey, requestHash) {
const lock = LockService.getScriptLock();
lock.waitLock(5000);
try {
const store = PropertiesService.getScriptProperties();
const existing = store.getProperty(eventKey);
if (existing) return JSON.parse(existing);
const reservation = { requestHash, state: 'RESERVED', createdAt: new Date().toISOString() };
store.setProperty(eventKey, JSON.stringify(reservation));
return reservation;
} finally {
lock.releaseLock();
}
}
This example is deliberately small. In a production design, move durable event history to an appropriate datastore, encrypt secrets, restrict administrative access, and define cleanup. The reservation record must not be mistaken for proof that dispatch succeeded. Only a stored provider response or verified lookup can establish acceptance.
Dispatch through a narrow, observable integration
The dispatcher should receive only approved fields: event key, recipient reference, program, country, budget, occasion, message template, language, and request hash. It should not receive the whole sheet row. Validate every value again at the boundary, sign or authenticate the request, set a short network timeout, and write a response record before changing the visible status.
Distinguish transport failure from business rejection. A timeout is unknown, not failed. A validation error is not retryable until the data changes. A quota response may be retryable after delay. An authorization error requires credential or scope repair and should not be hammered repeatedly. A provider acceptance means the request entered processing; it does not mean the recipient claimed a gift or that delivery completed.
Use exponential backoff with jitter for retryable errors, a maximum attempt count, and a dead-letter review queue. Every attempt should record event key, attempt number, timestamp, response category, safe error code, and next action. Do not store tokens, raw authorization headers, or unnecessary personal data in logs.
Apps Script quotas can change, and the official quota page states that a single script execution is limited to six minutes. Workspace accounts also have daily trigger runtime and URL Fetch quotas. Design the batch size from observed latency and leave margin. When the remaining execution time is low, save the cursor and schedule the next bounded run rather than trying to finish the entire sheet.
If volume, security, or recovery requirements outgrow Apps Script, keep the same data contract and move dispatch to a managed service with a durable queue. The form and sheet can remain familiar interfaces while the critical execution path becomes independently deployable, observable, and testable.
Build reconciliation and audit evidence from day one
An automation is incomplete until accepted requests are reconciled to final outcomes. Pull or receive status changes from the execution layer and update a separate status history, not just one mutable cell. Preserve accepted, invitation sent, claimed, shipped, delivered, failed, canceled, expired, refunded, and replaced events as applicable.
Reconciliation should answer four questions: Was every approved request dispatched once? Was every accepted request assigned an owner until closure? Does the financial amount match the approved budget and final outcome? Can a reviewer reconstruct who decided what without reading email or chat history?
Create daily exception views for approved-but-undispatched, unknown-after-timeout, accepted-without-progress, delivery-failed, canceled-after-dispatch, amount mismatch, and stale review. Assign severity and owner. A red cell without an owner and due date is decoration, not control.
Audit logs should avoid unnecessary personal data. Record stable references, actions, actors, timestamps, policy versions, hashes, and provider identifiers. Keep sensitive recipient data in the system designed to protect it. Apply retention separately to intake responses, review snapshots, dispatch logs, and fulfillment evidence. Deletion must not erase records that must be retained for legitimate financial or compliance reasons, but retention should not become indefinite by default.
Test restoration as well as deletion. Export or snapshot the schema, script version, trigger inventory, configuration references, and state definitions. A restored spreadsheet without its trigger owner, OAuth project, secret, and reconciliation job is not a restored service.
Worked case: employee milestone across three countries
Assume a company recognizes 5-, 10-, and 15-year anniversaries in the United States, Japan, and Germany. HR remains the authority for employment status and anniversary date. The program team owns the policy and budgets. Workspace provides controlled intake for exceptions and a review surface; the execution layer handles recipient invitation, choice, and fulfillment.
The monthly job receives a stable employee ID, milestone date, work country, preferred language, manager ID, and program code. It does not import a home address. The job creates an event key and checks whether the same milestone version already exists. Records with an inactive employee, missing country mapping, future termination before the recognition date, or unresolved manager move to manual review.
The manager sees employee name, milestone, country, standard budget, and message deadline. The manager can confirm or return the request, but cannot change the employee ID or raise the budget. Regional HR approves exceptions. After approval, the dispatcher sends the minimal payload with the event key. The recipient supplies delivery information through a controlled invitation.
Failure injection matters. Test a duplicate form submission, an Apps Script timeout after acceptance, a departed trigger owner, a revoked directory token, an unsupported country, a budget exhausted between review and dispatch, a recipient who never claims, and a delivery failure. For each test, define expected state, owner, evidence, and recovery action.
Acceptance evidence includes zero duplicate event keys, a complete approval history, successful retry lookup after an artificial timeout, no address fields in the review sheet, reconciliation of every accepted event, and documented access review. A pilot should use a small cohort and synthetic or consented test data before real milestone records are enabled.
Worked case: customer event with late changes
Assume a regional marketing team plans a customer roundtable for 120 invitees. The CRM owns relationship and contact eligibility; the event team owns attendance; finance owns budget; the gifting program owns policy and fulfillment. A form is used only for approved exceptions such as speaker gifts, replacement requests, or a changed market.
The event roster creates proposed requests with CRM contact ID, event ID, country, relationship owner, program code, and budget band. Marketing confirms business purpose and conflict checks. Procurement or compliance reviews higher-risk recipients according to company policy. The sheet does not import personal addresses from the CRM.
Seven days before the event, the system locks the main cohort version. Late additions receive a new roster version rather than silent edits. Cancellations before dispatch release budget reservations; cancellations after acceptance follow the execution layer’s cancellation rules. A guest who changes country returns to market review because availability, cost, and delivery timing may change.
Inject a partial outage: thirty requests time out while the execution layer actually accepts twenty. The correct recovery is not to resend all thirty. Query by idempotency key, mark the twenty accepted responses, and retry only the ten with verified absence. The reconciliation report should demonstrate that the final accepted count matches unique approved event keys.
Success is not “the script ran.” Success means every dispatched gift had a valid approval, no recipient received an unintended duplicate, exceptions had owners, financial totals matched, and personal information stayed in appropriate systems. Those criteria make the workflow defensible after the event team has moved on.
Roll out with reversible steps and a useful operating conclusion
Build the workflow in stages. First document boundaries and states. Next validate the schema with synthetic rows. Then connect read-only identity lookup, approval events, and a mock dispatcher. Add production credentials only after threat review. Run a limited pilot, reconcile every request manually, and compare the result with automated reports before increasing volume.
-
Name service, data, policy, budget, security, and operations owners.
-
Confirm the authoritative source for identity, eligibility, budget, and fulfillment.
-
Freeze the intake and review schema with versioning and protected control columns.
-
Register OAuth scopes, credential owners, trigger owners, and revocation steps.
-
Implement event keys, request hashes, locks, bounded retries, and lookup-before-resend.
-
Test duplicate, timeout, quota, authorization, cancellation, and delivery-failure cases.
-
Define retention, deletion, access review, backup, and restoration evidence.
-
Pilot with a small cohort and reconcile every accepted request to closure.
When should the team move beyond Apps Script?
Move the critical dispatch path when execution limits, concurrency, security controls, deployment discipline, regional requirements, or recovery objectives exceed what the script can reliably support. Keep the familiar form and sheet if they still help users, but place durable queues, secrets, logs, and integration logic in managed services with explicit ownership.
The durable pattern is not “Form to Sheet to gift.” It is governed intake to versioned approval, idempotent dispatch, and evidence-backed reconciliation. Google Workspace is valuable because it gives teams an accessible interface; it is safe only when each component has narrow authority and failure does not invite guesswork.
For organizations that have approved events but need a global execution layer, Giftpack can receive a controlled, minimal dispatch payload and coordinate recipient choice and fulfillment. It does not replace Workspace administration, identity governance, consent, tax, payroll, legal review, or employer decisions; those responsibilities remain with the organization and its advisers.